Signals sites use
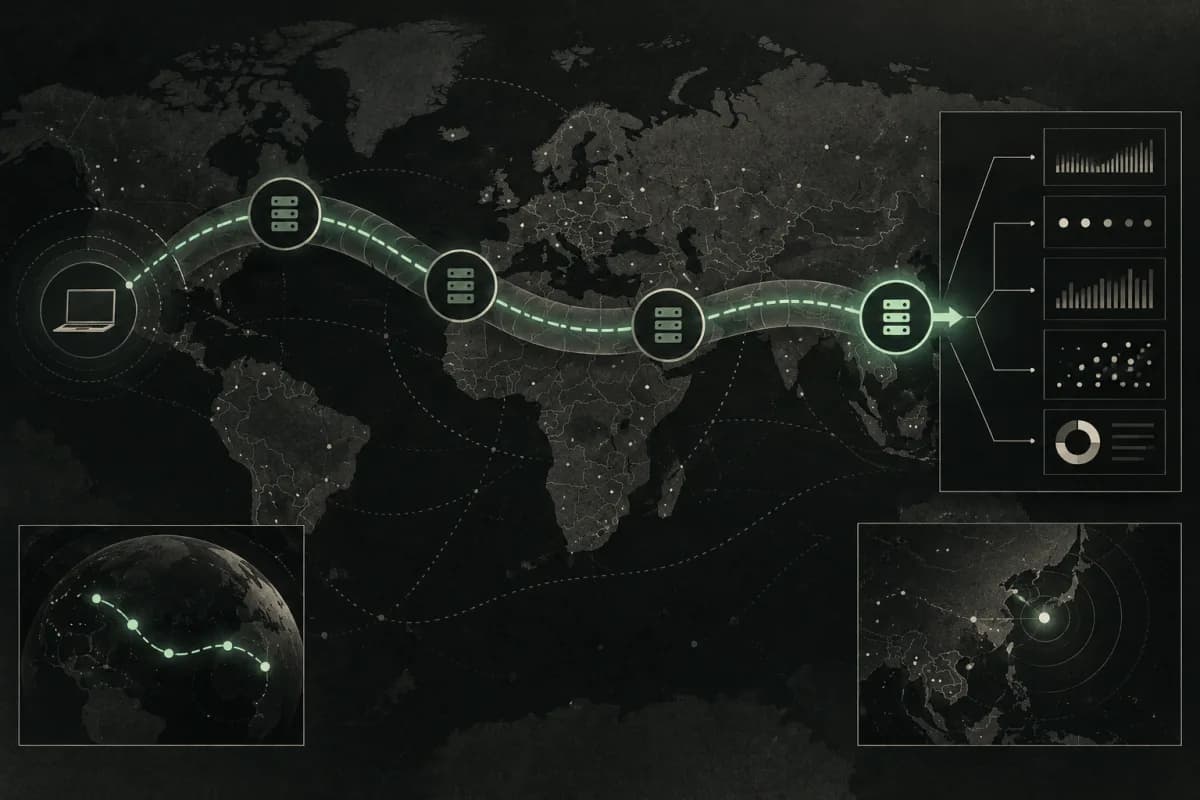
IP reputation: whether the address belongs to a hosting provider, a known VPN operator, or a published Tor exit node. Tor exits are public, so Tor detection is close to certain. VPN and proxy detection rely on commercial databases and heuristics.
Consistency checks: a browser time zone or language that does not match the IP's country, a desktop browser arriving from a mobile carrier, or a browser user agent coming from a datacenter ASN.
Protocol signals: TLS and HTTP fingerprints that do not match the claimed browser, or headers that real browsers always send but automation tools omit.
Why results are probabilistic
Residential proxies route traffic through real home connections, so their IPs look residential. Conversely, a person on a corporate network or a travelling user can trip consistency checks innocently. Good tools report likelihood, not verdicts; this site shows Known, Likely, Inferred or Unavailable next to each signal.