The practical difference
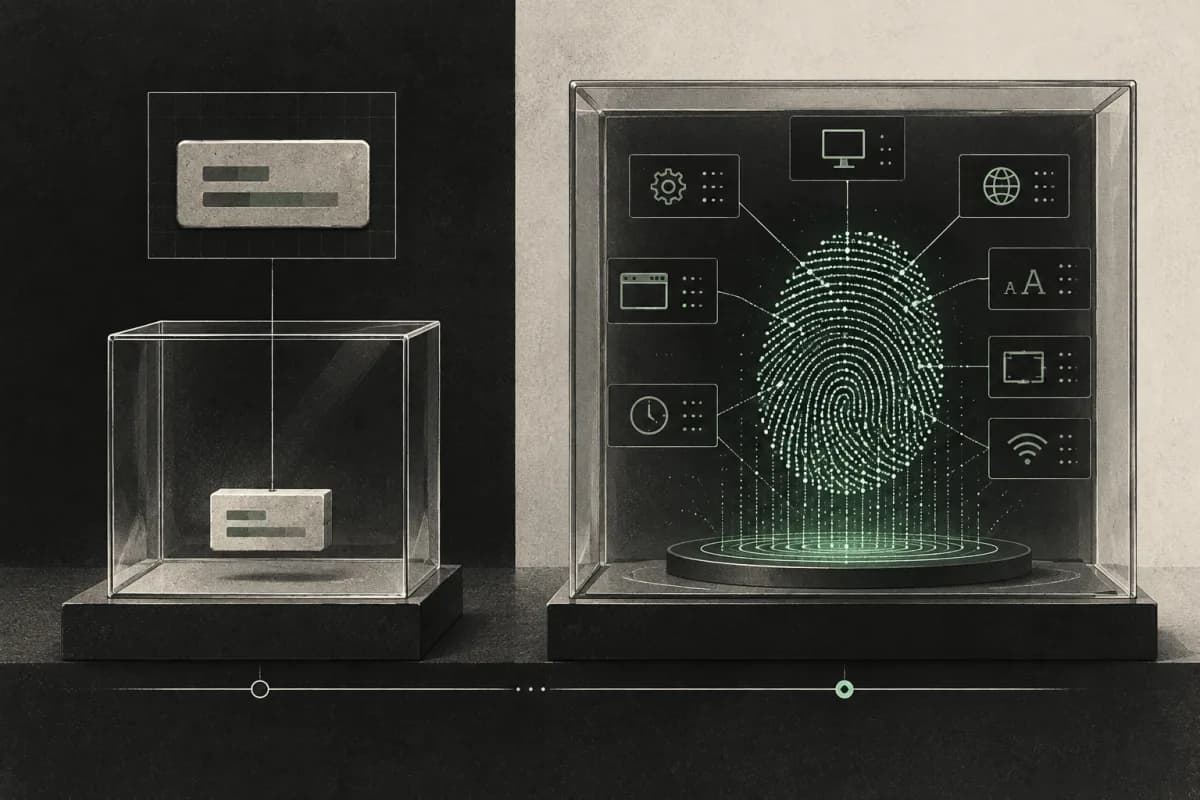
A cookie is a value a website asks the browser to store and return later. A browser fingerprint is calculated again from characteristics the browser exposes each time a page runs the collection code. Cookies are explicit local storage. Fingerprints are repeatable observations.
That difference changes how they fail. Clearing site data removes ordinary cookies, but it does not necessarily change fonts, graphics behavior or the browser timezone. A browser update can change a fingerprint while leaving a cookie untouched. Neither method is perfectly permanent, and neither method identifies a human by itself.
How cookies recognize a browser
A server can create a random identifier, place it in a first-party cookie and associate it with a session or account. On later requests to the same site, the browser returns the value. This is reliable until the cookie expires, the user clears it, the browser blocks it or the request happens in another profile or device.
Cookies are well suited to sessions, saved preferences and signed-in experiences because the browser and server have an explicit storage mechanism. Security settings such as HttpOnly, Secure and SameSite also make their behavior reasonably understandable. Cross-site tracking cookies face much stricter browser restrictions than first-party cookies.
How a fingerprint recognizes an environment
Fingerprinting collects values such as canvas rendering, WebGL capabilities, audio processing, fonts, screen dimensions, language and timezone. A library normalizes those values and produces an identifier or set of component hashes. On a later event, the application repeats the collection and compares the result.
The identifier may continue after cookies are cleared because it was never stored as a cookie. It can also change without user action when software, hardware or privacy protections change. Browsers such as Tor Browser try to make many users look alike, while others may randomize selected outputs so repeated tests are deliberately inconsistent.
Why products often use both
For a signed-in session, a secure cookie is usually the straightforward choice. A fingerprint can add context when a sensitive event occurs, when a trial is requested, or when an application needs to notice that cleared storage did not create a truly new browser environment. It should not replace a well-designed authentication session.
Using both also gives a product clearer failure modes. A known session arriving from a changed fingerprint may deserve a step-up check. A familiar fingerprint with no cookie may simply be a returning visitor who cleared storage. The action should reflect the whole event rather than the presence or absence of one identifier.
Consent, disclosure and data minimization
Cookies and fingerprints can both fall under privacy and electronic-communications rules. The requirements depend on purpose, jurisdiction and whether the method is strictly necessary, used for security or used for tracking and advertising. Changing the technical method does not remove the obligation to understand the purpose.
A responsible implementation collects only at meaningful decision points, explains the security or abuse-prevention use, limits retention and avoids sharing a universal identifier across customers. Teams should obtain legal advice for their own use case instead of assuming that a hash is anonymous or that security language automatically makes every collection necessary.